Fundamentals of Smart Contract Security Released


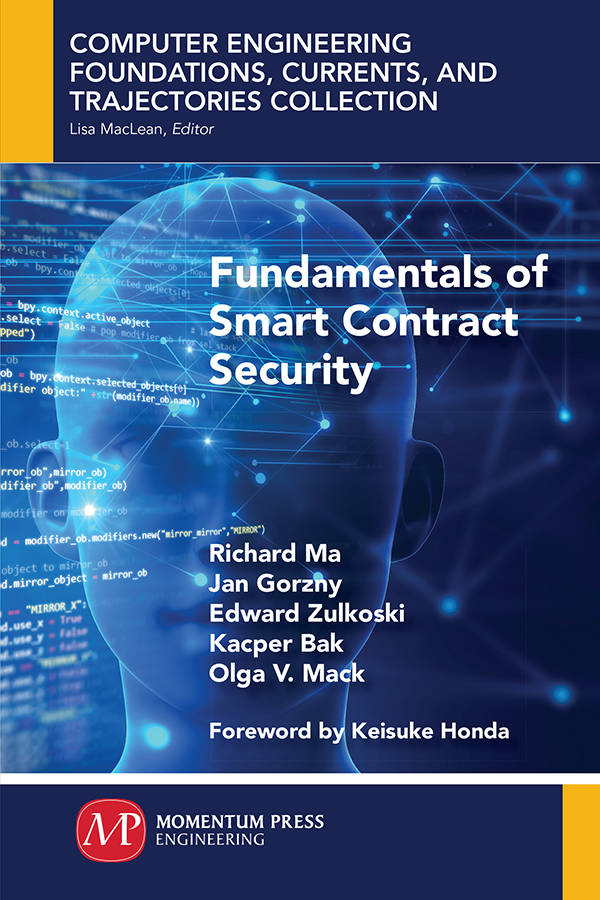
Fundamentals of Smart Contract Security, the world’s first book dedicated to the subject of the security of blockchain applications, has been released. The book is written by smart contract security experts at Quantstamp.
Security is Essential for Blockchain Applications
While blockchains themselves are often secured by large amounts of hashpower, applications running on top of them, in the form of smart contracts, can be subject to coding errors or security vulnerabilities just like any other software. Unlike regular software though, smart contracts are often directly in charge of assets, and once they are written to a blockchain, they cannot be changed. In some cases, the smart contract code also is viewable by others accessing the blockchain. This makes secure smart contract development essential.
Written by Smart Contract Security Experts
Quantstamp is a Y Combinator-backed blockchain security company which has audited over $800 million worth of smart contracts. We are among the first to have built a decentralized automated smart contract security analyzer network deployed on the worldwide Ethereum blockchain and our team has 5 PhDs, including security and formal verification experts.
Actionable Advice
Fundamentals of Smart Contract Security provides actionable advice on blockchain security. It goes beyond theory, giving real practical advice, including common vulnerabilities detected in the wild, and best practices for secure smart contract development.
“Smart contracts and programmable money enable a wealth of new possibilities, but their immutable and public nature means security must be given top priority. This book will teach you how.” - Eric Ly, Co-founder, LinkedIn, and CEO of Hub Token
Buy the Book today
Fundamentals of Smart Contract Security is available for order today at Amazon.com as well as Momentum Press.
Sample chapters of the book can be read online here, courtesy of Momentum Press.
About Quantstamp
Quantstamp is a Y Combinator-backed blockchain security company developing automated security tools such as the Quantstamp protocol and also conducts expert smart contract audits. Powered by QSP, the Quantstamp protocol aims to enhance smart contract security and the reputation of projects that create smart contracts by producing openly accessible security reports.